Certification
ISO/IEC 27001 certified.
RazorERP is certified to ISO/IEC 27001:2022 by DQS Inc. Download the certificate and review the certified scope as part of your security evaluation.
CERTIFICATE 31619142 ISMS22 · PDF
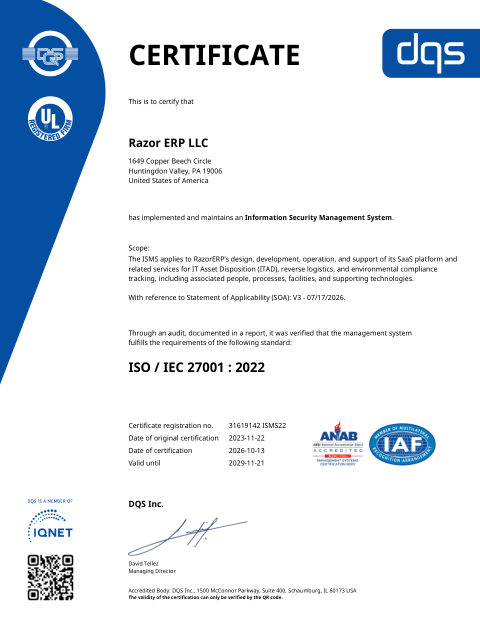
Certificate details
Using it in your security review
- 01Download the certificate and share it with your reviewers
- 02Check that the certified scope covers the services you will use
- 03Verify the certificate by scanning its QR code, which DQS states is the only way to verify it
- 04Request questionnaire responses, the SLA, and other documents if your review needs them
CERTIFICATE · PDFDownload the ISO/IEC 27001 certificateCertificate 31619142 ISMS22, issued by DQS Inc. and valid until 21 November 2029. Share it with your reviewers as it is.Download the certificateRequest other security documents →
What ISO/IEC 27001 certification means
ISO/IEC 27001 is the international standard for information security management systems. Certification means an independent certification body has audited how an organization identifies information security risks and manages them through policies, controls, and continual review.
Certification applies to the scope stated on the certificate. Read the scope alongside our security review topics to understand which services and locations are covered. ISO itself does not issue certificates; they are issued by certification bodies.
Questions to bring to your review
- Does the certified scope cover the services you will use?
- Which controls in the Statement of Applicability matter most to your review?
- How are risks identified and reviewed between audits?
Need more for your security review?
Tell us what your review requires and we will share the documentation.